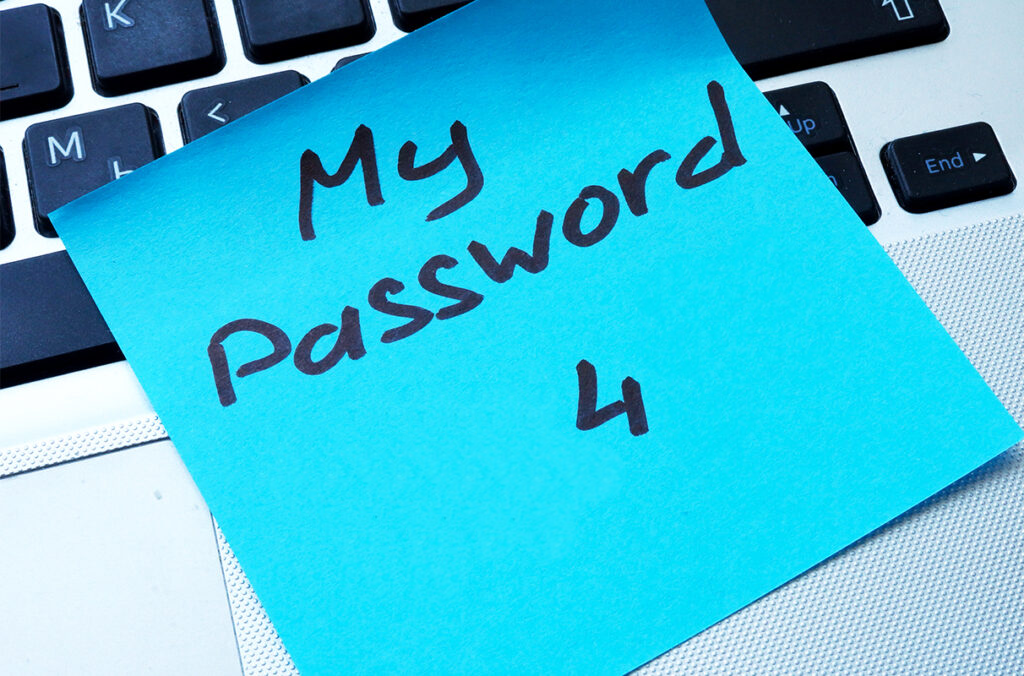
Good to see they followed best practices by using a random number. At least it wasn’t a birthdate.

Only way you could have made this better is if it was in PHP.
FYI, it’s an xkcd.
It’s amazing, I have the same combination on my luggage!
What is this joke?
A security certificate authority from India had several of their keys deciphered because the numbers used to generate them were way too short. In fact one of them was simply the number 4. Because of this basically the entire internet has been put at risk because it’s trivially easy to forge keys from this trusted authority.
As I understood it a certificate authority (the thing that you trust to make sure a website is who it claims it is) used 4 as the “password” for their cryptographic key, which would make it quite easy for a malicious attacker between you and a legit website, to modify the contents, encrypt it with their own key and then send their own certificate of, looking like it came from a certificate authority that you trust, essentially enabling an attacker to break encryption. (for example an ISP could do this as all the traffic goes through them)
Its the same joke everyone else is making.
If you open the original post URL, there is an image with a post-it note reading “My password 4”. Some servers don’t show the post images sometimes, I had to open the original URL to see the picture.
Yeah kbin.earth doesn’t show it.
Ah sorry about that the picture is necessary
Discord will regularly delete images you link to, so I wouldn’t use them as a link
I rarely upload and didn’t save it just copy pasted when I made it quick in gimp.
I will keep it in mind though.
It’s fine, I visited the original link and came back to reply to you, because of the dv you got. People are wild.
don’t forget the leading 115 zeroes.
It’s a perfect addition to the HTTPV ecosystem! https://www.youtube.com/watch?v=M1si1y5lvkk
deleted by creator