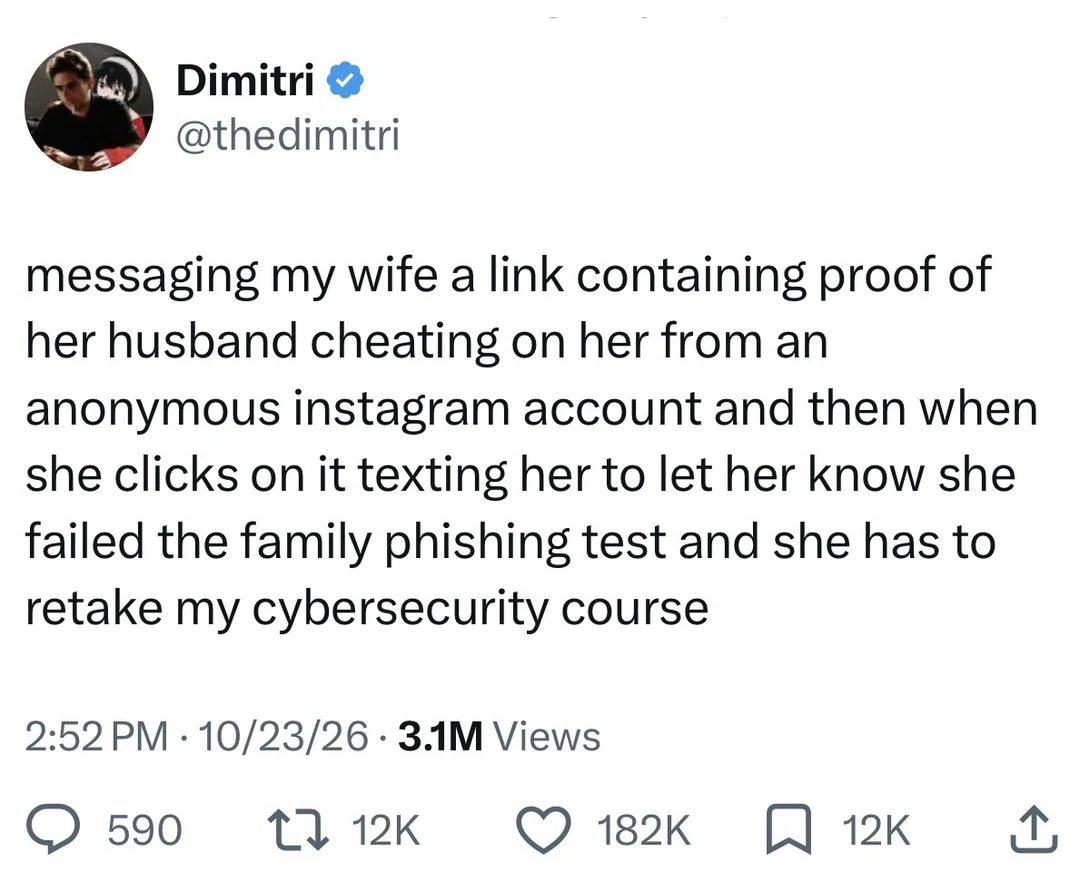
The thing is, a link in an email is not any different than a link here on Lemmy, yet we click on those all day. Yes, both could lead to a malicious website, and if you don’t have a recent web browser, then you could get in to trouble without any action.
IMO, the only reason why there is a focus on phishing simulation in orgs is because email is something IT owns and you can easily track who does and doesn’t open an email. If there is a legitimate concern with opening random links, then phishing simulations would also extend to maybe peppering fake links on LinkedIn or other places where IT thinks their co-workers are browsing, but no one (AFAIK) does this.

The thing is, a link in an email is not any different than a link here on Lemmy, yet we click on those all day. Yes, both could lead to a malicious website, and if you don’t have a recent web browser, then you could get in to trouble without any action.
IMO, the only reason why there is a focus on phishing simulation in orgs is because email is something IT owns and you can easily track who does and doesn’t open an email. If there is a legitimate concern with opening random links, then phishing simulations would also extend to maybe peppering fake links on LinkedIn or other places where IT thinks their co-workers are browsing, but no one (AFAIK) does this.