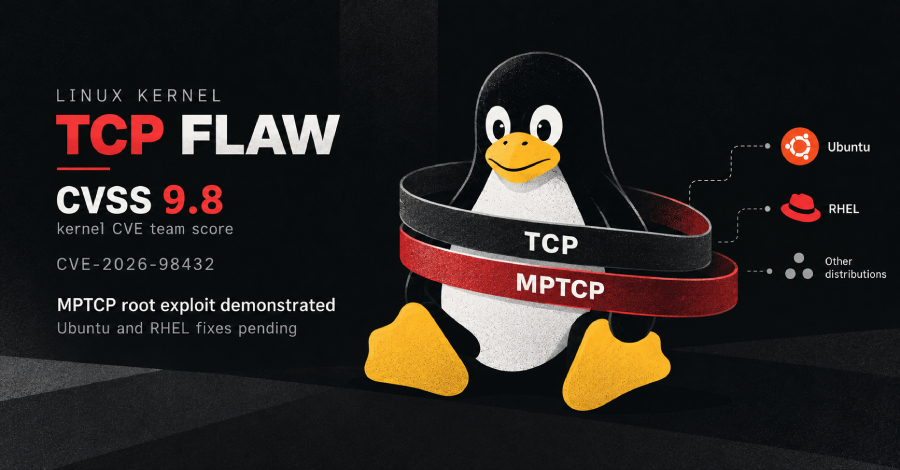
Every Go application since 1.24 will activate MPTCP on their sockets by default.
And I’ve read that this includes Syncthing, which is why I’m posting this here
You must log in or register to comment.
Does unattended upgrades fix this on Debian? Or do I have to reboot now for it to take effect?
Depends on your settings. You need to reboot for kernel upgrades, so you’re good if you have automatic periodic reboots configured and kernel updates applied unattended.
Could everyone stop blowing holes in things please, spent all yesterday rebuilding internet facing servers.
On the plus side, everything will be up to date. So there’s that
Also with both this kernel and the php thing, Debian had a fix way before the big corporations. Even Amazon
Is it known if/ when Ubuntu is going to provide a fix? https://ubuntu.com/security/CVE-2026-98432 Rn the page states: work in progress for a fix.
Someone rated the issue as 9.8.Other distributions provided a fixed kernel package 10days ago. Some say, Ubuntu engineers do not rate the issue as critical. But there are exploits available which prove a DoS. Not sure if the RCE with privilege escalation has an exploit yet and under which circumstances the RCE works. Is a golang service required? Are other services affected - is multipath TCP sufficient? Does the issue affect ipv6 too?
DoS isn’t that bad. RCE with root + an exploit on the other hand. Um…
From what I read about regarding the PHP vulnerabilities, the RCE was extremely difficult to pull off. I’d guess it’s the same here, at least until some non-AI companies weigh in, since these AI companies tend to distort the reporting and severities quite a bit.
Thank you.
Difficult as in unlikely that the exploit works or difficult to write an exploit? The latter doesn’t help me much. :)
Regarding the php2shell issue: a lot of admins took their services down until it was patched. It’s more a decision based on a guess - big number bad, evil acronym scary - than actually understanding what the exploit does. One can either believe it or not.
And that’s the thing about the recent exploit (multipath TCP): I can’t evaluate myself, whether the issue is likely an exploitable RCE. That is one factor missing in risk assessment: is the outcome potentially fatal? Yes, rce and priv escalation. Is it likely? I can’t tell.
I’m sorry. I don’t mean to doubt your expertise. I simply don’t know you. It is the same with hackernews, the author repeats what he’s or she’s told. (Good overview article though. Thanks again for it.) RN It’s: Someone from the internet said don’t panic. A link to a statement from the Ubuntu package maintainer or distribution would make me feel at ease. I still couldn’t make sure for myself - a lack of time and competence in the field - but I would trust it.
Difficult as in unlikely that the exploit works or difficult to write an exploit?
Difficult as in it’s a race condition that can theoretically be exploited when you get the timing right. But timing, if it’s not on a well-known isolated system right before you in some lab, depends on a million details, some –once we are talking about real-life examples– outside your control.
Yes. Anthropic wrote: it took them like an hour to get it right on their lab system. That’s different than the wild wild internet.