The score sounds a bit overblown considering this is for MPTCP which is as far as I understand rarely used? And it sounds like the chance of this leading to anything more than a crash is low. But whatever.
It’s a data race. Memory safety is still super important for security.

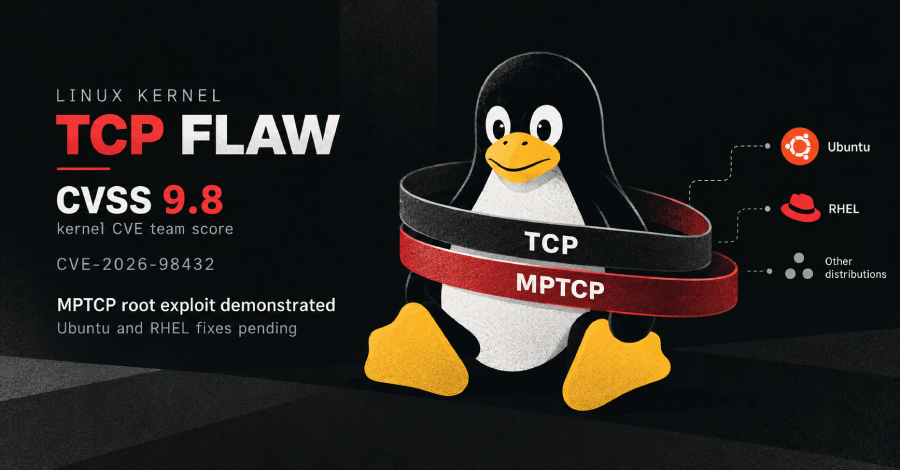
The score sounds a bit overblown considering this is for MPTCP which is as far as I understand rarely used? And it sounds like the chance of this leading to anything more than a crash is low. But whatever.
It’s a data race. Memory safety is still super important for security.
Every Go application since 1.24 will activate MPTCP on their sockets by default, so it’s in fact quite widely used.
Many orgs consider the rating overblown. While the impact is devastating, the attack is hard to pull of.
They’re able to issue shell commands as root.