
You must log in or register to comment.
Ai adoption is going great I see
of all the things i hate about LLMs, getting vulnerabilities in important software like linux discovered and fixed is not one of them
Yeah. As horrible as LLMs are in many ways, finding vulnerabilities is something they’re great at.
It’s absolutely a good thing that a good actor with an LLM finds a vulnerability before a bad actor with or without such tools.
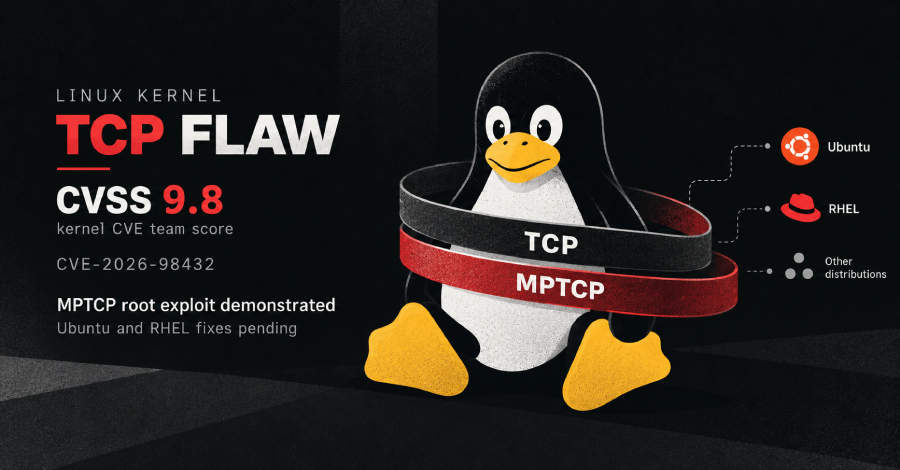
The exploitable code has been in the kernel since 4.4…
Fuck LLMs and the horse they rode in on but I have to admit the vulns and decompiling capability of them is pretty impressive.
On Linux, an application must request MPTCP when it opens a socket.
Ah nothing to worry about.
As of Go 1.24, Go programs do so by default for the sockets they listen on
Fuuuck
With the rate of CVEs coming up, feels like I’ll have to switch to nixpkgs staging and just compile everything myself gentoo-style for my server.
If you build your own kernel, the fix is in Linux 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10 and 7.3
If you can’t build your own kernel, store-bought is fine.
Fedora is at 7.2.13 today, so all good (so long as dnf-automatic is doing it’s thing and auto reboots are enabled).