You must log in or register to comment.
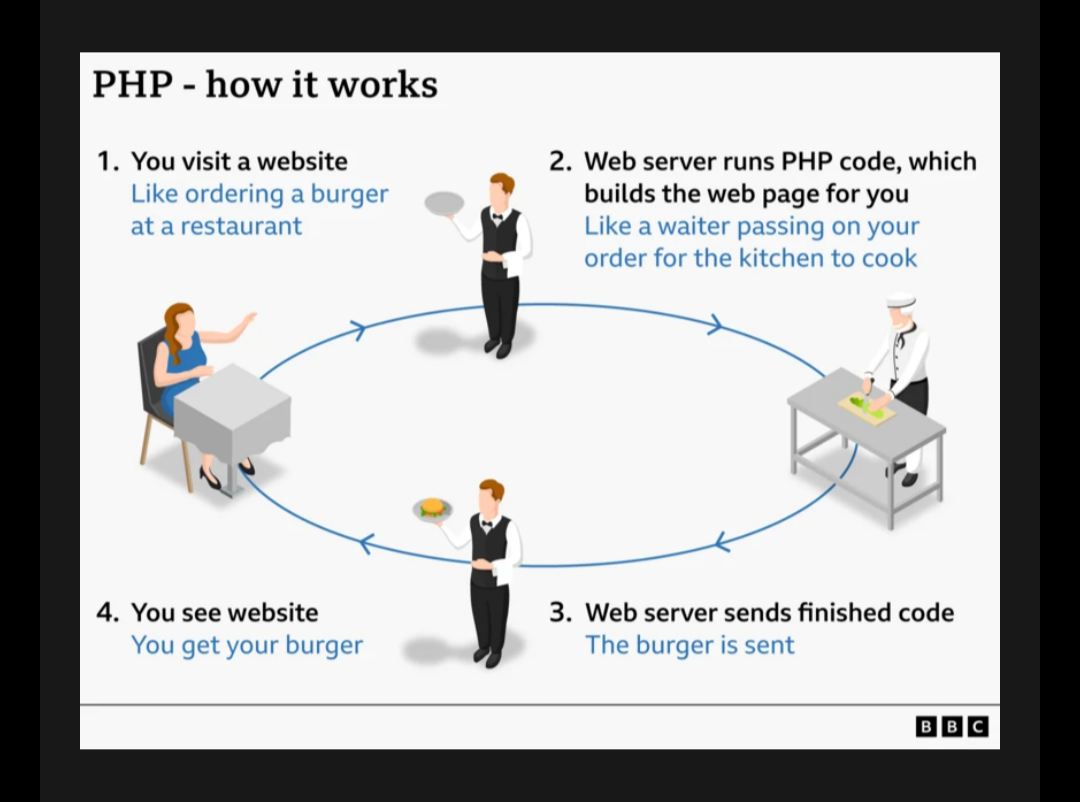
What if I visit a website to order a burger
The cook should be represented as the database.
Back in the 80’s, my brother “hacked” a pizza place because he knew how they wrote green olives and black olives on their ticket. He dated a girl who worked there for a stint.
I don’t remember how it worked and he has since passed, but it was something with the order that he would list the toppings that would fuck up the cook, so the order always came out wrong and boom! Free pizza.
Step 5. you inject poison in your burger and send it back. Causing the cook to die and you take over as the owner of the restaurant
the person getting the burger actually has a user agent which fetches the burger for them. Its a food delivery app and the browser is doordash/uber eats etc. Instead of packets its human beings who read a screen and understand obligations.
How it should work for 99% of websites.
CSS didn’t do shit wrong:
Love this one. Only thing I don’t get is why so many people can’t stand high contrast. Or even go so far as to say white background hurts their eyes. Black on white is just fine, thank you very much. And if it is too harsh, then I suspect that actually either one’s monitor is too bright, or - more likely - the environment they’re in is too dim.
Can we get Samuel L. Jackson to read it for those with vision impairment?
most people who have seen the old internet probably feel this rage
Ublock blocks this for some reason
EDIT turns out the reason is it appears to be infected with a botnet
Not in Librewolf, at least. Ublock and Noscript enabled. Site still shows.
Adguard blocks it. Adguard usually is more trustworthy
You probably don’t have these filter lists enabled: 📒 HaGeZi - Multi PRO mini 🔐 HaGeZi - Threat Intelligence Feeds - Mini
That’s weird. I did some digging and can’t find its name, ip, or hosting company servrex.com on any block list. I checked HaGezi on github based on your post.
I used this https://github.com/hagezi/dns-blocklists#listlookup and searched https://motherfuckingwebsite.com
If you search the closed github issues, you’ll see more details for the url
Which list? I searched the Multi Ultimate Full list and it wasn’t there.
Well that’s even weirder. It is in a list labeled malicious/scammer/fishing.
It absolutely isn’t any of those.
Someone else claimed it pulls resources from a botnet but if you view source, that isn’t true.
Can ypu add to the github issue asking to review it?
Well, I didn’t check its internals.
4
Dam, I guess I was a programmer at KFC, and I didn’t even know it…
Wait till you learn about this new CGI thing, you’ll be amazed about what it can do: https://en.wikipedia.org/wiki/Common_Gateway_Interface
I doubt it will cook burgers for you though 😕 😔 🍔🍴🤤
For some reason I am hungry all of a sudden…
Why is everybody talking about PHP lately? Am I out of the loop?
To add what the others said, yesterday morning there was news that every php version is vulnerable but the fixes were published very late in the day (or whenever depending on timezone) thus there was a 8+hours of unceartiny and fear for administrators. A lot of websites shut down due to that.
Most of my experience with PHP is from pen testing so most of my orders look something like <?
$_GET[0]?>