When they first started doing these tests unannounced, our IT department got a horrendous failure rate and then management had to announce that if we recognize it as a phishing simulation, we should still report it, and we also shouldn’t start poking around in the supposed phishing links. 😅

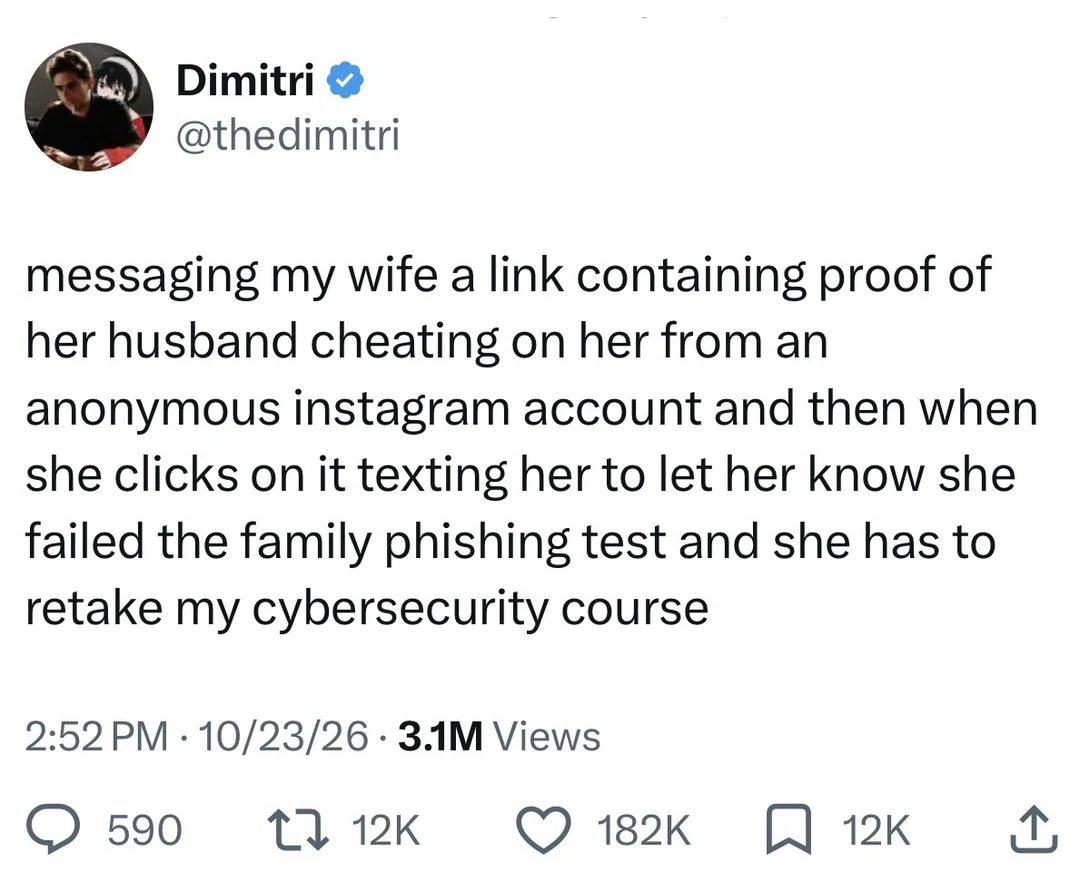
If we don’t report the emails as phishing it is considered a fail.
When they first started doing these tests unannounced, our IT department got a horrendous failure rate and then management had to announce that if we recognize it as a phishing simulation, we should still report it, and we also shouldn’t start poking around in the supposed phishing links. 😅
I report so many things from executive level because all of the training examples use exec comms as an example.
I’ll delete the failure report without reading that either.
…and then you don’t get into company Harvard, or what?